Did El Niño turn Hurricane Polo into the most powerful storm of the season?
The BBC's Courtney Sargent explains how El Niño could have rapidly turned Hurricane Polo into one of the Pacific season's most powerful storms.
Read moreSep 23, 2026
DYOPATH has published an hour-by-hour framework for organizations responding to a data breach, covering containment, evidence preservation, notification order, and recovery—timed guidance designed to reduce the confusion that typically slows the first 24 hours.

Oakbrook Terrace, United States, September 23, 2026 /NewsNetwork/ -- DYOPATH's advice for a company that discovers it's been breached is blunt: stop, isolate the affected machines from the network, and call an incident response provider's emergency line. DYOPATH's own incident response team is staffed 24/7 at 1-866-609-PATH. The company published a full hour-by-hour framework this week (https://dyopath.com/first-24-hours-after-a-breach/) for everything that follows.
The first 60 minutes decide how much worse things get. The instinct is to fix everything at once; the guidance says resist it. The only job in the first hour is to stop the bleeding without destroying evidence needed later. Pulling the network cable or disabling Wi-Fi on a compromised machine is almost always better than shutting it down completely, since powering off erases the data in memory, and that memory is often exactly what a forensic investigator needs to trace how the attacker got in. Passwords change on any account known to be involved, starting with admin rights. Multi-factor authentication doesn't get disabled to make troubleshooting easier, since that's exactly what an attacker wants. Nothing goes out company-wide yet; a vague "IT issues" message that leaks before the scope is understood tends to cause more confusion than it prevents.
Hours one through four are for preserving evidence, not cleaning up. Photograph ransom notes and error messages with a phone camera rather than screenshotting them, since screenshots can be altered, questioned, or lost if a machine reboots. Exact timestamps get logged. Firewall and endpoint logs don't get cleared or overwritten by anyone trying to help. NIST's Computer Security Incident Handling Guide (SP 800-61) lays out the standard for this kind of evidence handling, including chain of custody. Most companies without a forensics team on retainer bring one in around this point, since running a full investigation for the first time, mid-incident, tends to cost more time than it saves.
Three calls matter most in the next window, and the order isn't arbitrary: legal counsel, the cyber insurance carrier, then an incident response provider if one isn't already engaged. Counsel goes first, since attorney-client privilege affects what gets documented, and notification law varies by state and by the type of data involved. The insurer comes second; most cyber policies require notification within a set window, often 24 to 72 hours, and may require using their approved vendors, so calling after a provider's already engaged can mean the costs aren't covered. Federal reporting sometimes applies too, per CISA's incident response resources, and involvement from the FBI's Internet Crime Complaint Center is sometimes protective rather than complicating. Regulators and insurers generally respond worse to a late or hidden notification than a prompt, honest one.
Communication comes next, employees first, in plain language, before a headline or a customer breaks the news instead. A customer or partner notice usually goes through legal review before it goes out, and it can be short. One line in the framework stands out: don't promise "no data was affected" before that's confirmed, since sentences like that tend to get quoted back later.
Recovery starts once containment is confirmed, not assumed. A system restored and reconnected before the entry point is actually closed often gets compromised again within days. DYOPATH notes that organizations with a written incident response plan in place move through these hours noticeably faster and calmer than those improvising for the first time, not because the situation is less serious, but because nobody's arguing about who calls the insurer while the clock is running.
About DYOPATH:
DYOPATH has kept organizations' technology running since 1996, formed from the merger of DYONYX and Single Path. Today, its team of more than 600 U.S.-based people supports businesses across the United States and Mexico. Learn more at https://dyopath.com/about-it-company/.
Contact Info:
Name: Charles Orrico
Email: Send Email
Organization: DYOPATH
Address: 1801 South Meyers Road, Oakbrook Terrace, Illinois 60181, United States
Website: https://dyopath.com/
Source: NewsNetwork
Release ID: 89204227
In the event of encountering any errors, concerns, or inconsistencies within the content shared in this press release, we kindly request that you immediately contact us at [email protected] (it is important to note that this email is the authorized channel for such matters, sending multiple emails to multiple addresses does not necessarily help expedite your request). Our dedicated team will be readily accessible to address your feedback within 8 hours and take appropriate measures to rectify any identified issues or facilitate press release takedowns. Ensuring accuracy and reliability are central to our commitment.
The BBC's Courtney Sargent explains how El Niño could have rapidly turned Hurricane Polo into one of the Pacific season's most powerful storms.
Read moreThe private email address GitLab gives you for filing issues by email is a credential. Anyone who gets it can email a patch that GitLab commits in your name, to any branch you can push to, including main, and can start CI/CD jobs that run as you. GitLab shows each user this address behind a button labeled "Email work item to this project." Mail sent to it opens an issue in that project, authored
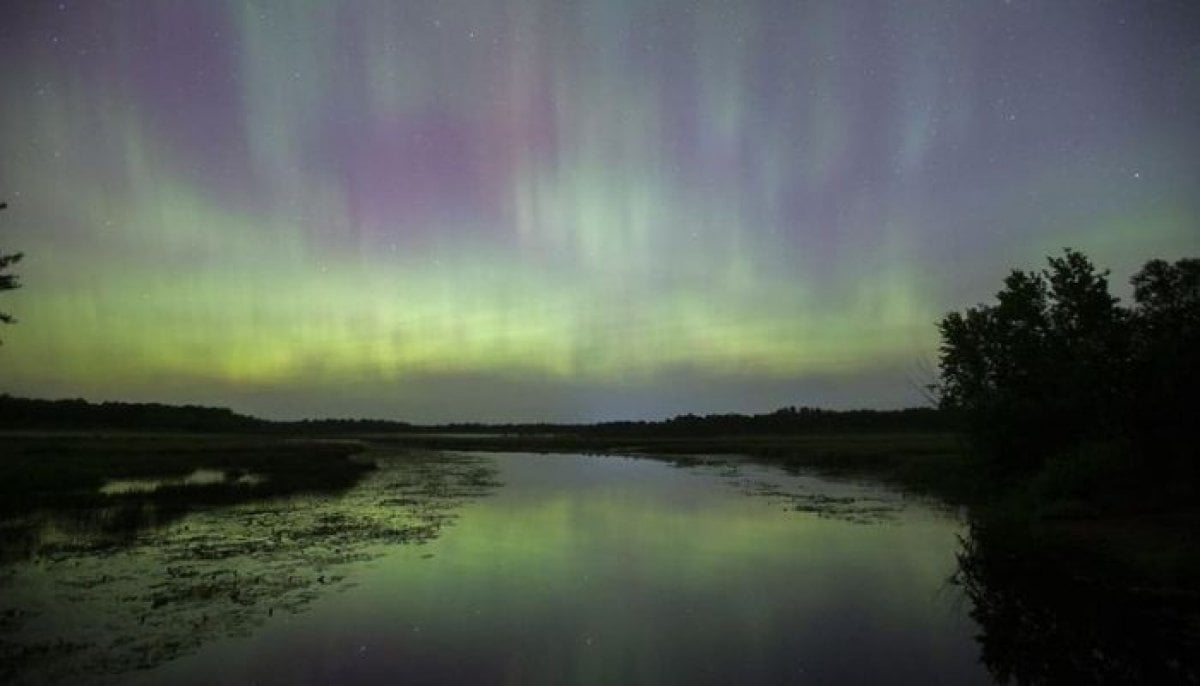
Read moreNorthern lights could light up skies across 22 US states tonight: How to watchThe autumn equinox has officially arrived bringing lighter or more intense hues. A stream of solar wind could head our way to bringing an aurora glow. On late Wednesday, this is expected to stir Earth’s magnetic...
Read moreStock in major firms such as Microsoft, Nvidia and SpaceX was bought and sold on behalf of the US president.
Read moreSeptember's full Moon will rise across on Saturday 26 September. The best viewing conditions currently look to be across southern and eastern parts of the UK.
Read moreGrowers are facing losses of £10m, as 30 million heads of lettuce will be rendered unusable.
Read moreTwo MikroTik RouterOS SSH vulnerabilities chained together let attackers take full administrative control of Internet-exposed routers without a password, SSH key, or completed authentication. The chain, which CERT Polska calls MikroTrick, combines an SSH state-machine flaw (CVE-2026-67279) with an argument-injection bug in the RouterOS login process (CVE-2026-86060). Attack logs date to at
Read moreThe regulator says it has concerns over how the site is relying on third party checks provided by Apple for some users.
Read moreSelf-driving systems are getting so good that drivers may overestimate the technology and not be prepared to respond when something goes wrong.
Read moreEnergy Secretary Chris Wright is pitching a future of fossil fuel abundance. It’s not always an easy sell while war drags on and oil prices surge.
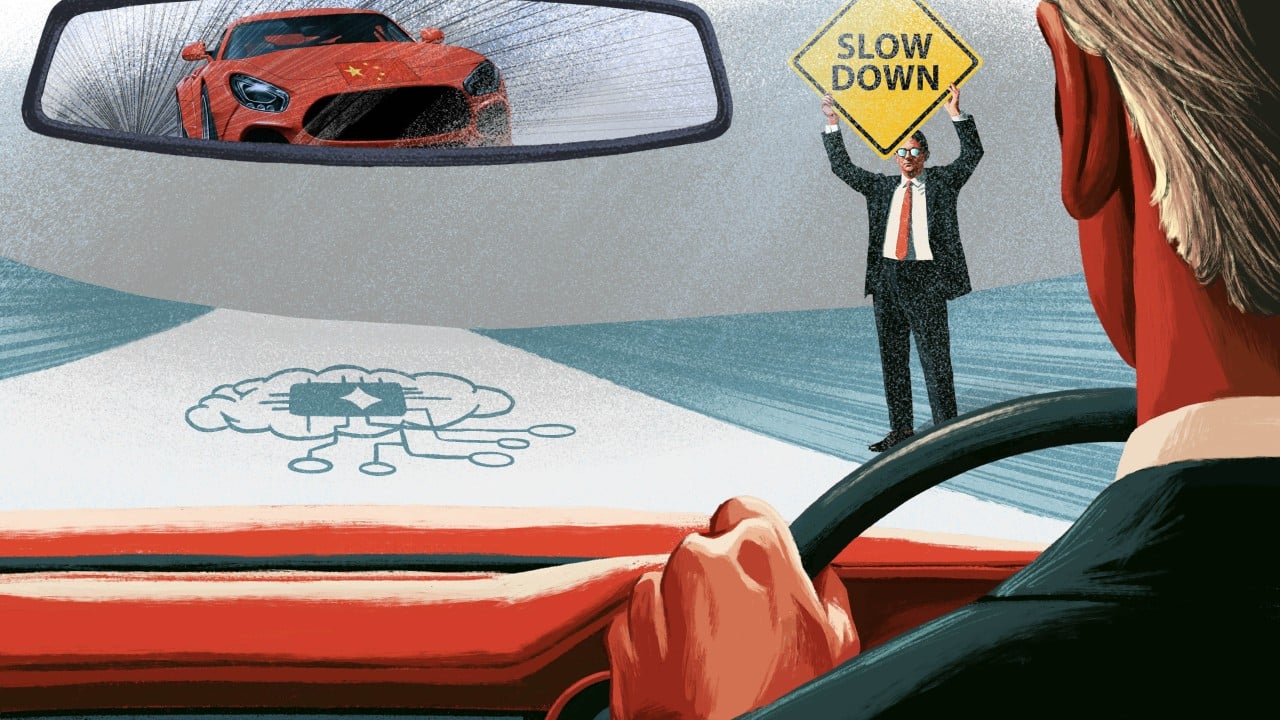
Read moreWhen the presidents of the United States and China meet in Washington, the world will be watching to see whether their two countries can make good on their agreement to work towards “constructive strategic stability”. In the sixth part of a series, Chong Ming Lee and Vincent Chow examine what’s behind the call for “pacing” by American AI giants – effectively a slowdown in development – and how the phenomenon is being viewed in China. After years of rapid development, leading US AI executives are...
Read moreIt's a question many couples grapple with - how many children should you have? Now, a study has revealed that if you want to be truly happy, two daughters should be your goal.
Read moreYOUR NEWS, OUR NETWORK.
Do you have Great News you want to tell the world?
Be it updates about your business or your community, you can make sure that it’s heard by submitting your story to our network reaching hundreds of news sites across 6 verticals.